leakfix
An open-source CLI that replaces a leaked secret without taking the app down, and undoes everything if any step fails.
Open source under the MIT licence. The code, tests and every design decision are public on GitHub.
The problem
I pushed the .env file of one of my own apps to a public GitHub repo: the MongoDB password and the JWT secrets, readable by anyone. Deleting the file doesn't help, because it stays in the git history and bots scan new commits for credentials within minutes. The only real fix is to rotate: replace every secret so the leaked one stops working.
Finding a leak is the easy part; GitHub even emails you. Fixing it is a fiddly sequence across several dashboards, and doing it in the wrong order takes production down. Delete the old database user before the app has switched, and every request fails. Most small teams have no tool for this step, so they either rush it or leave the leaked secret alive.
How a rotation works
- 1
Prepare
Create a new credential next to the leaked one, so both work for a moment. For MongoDB Atlas that's a new database user with exactly the same roles; for a JWT secret, a new random value.
- 2
Switch
Put the new values into the deployment's environment variables on Vercel or Render, remembering the old ones so they can be restored.
- 3
Redeploy once
One production redeploy for all changed variables, then wait until the new deployment is actually serving traffic.
- 4
Verify
Call the app's health route. If the app can't reach its database with the new credential, this is where it's caught.
- 5
Revoke
Only now delete the leaked credential. Every step is written to an audit log that never contains a secret value.
Key decisions, and why
Everything before revoking can be undone
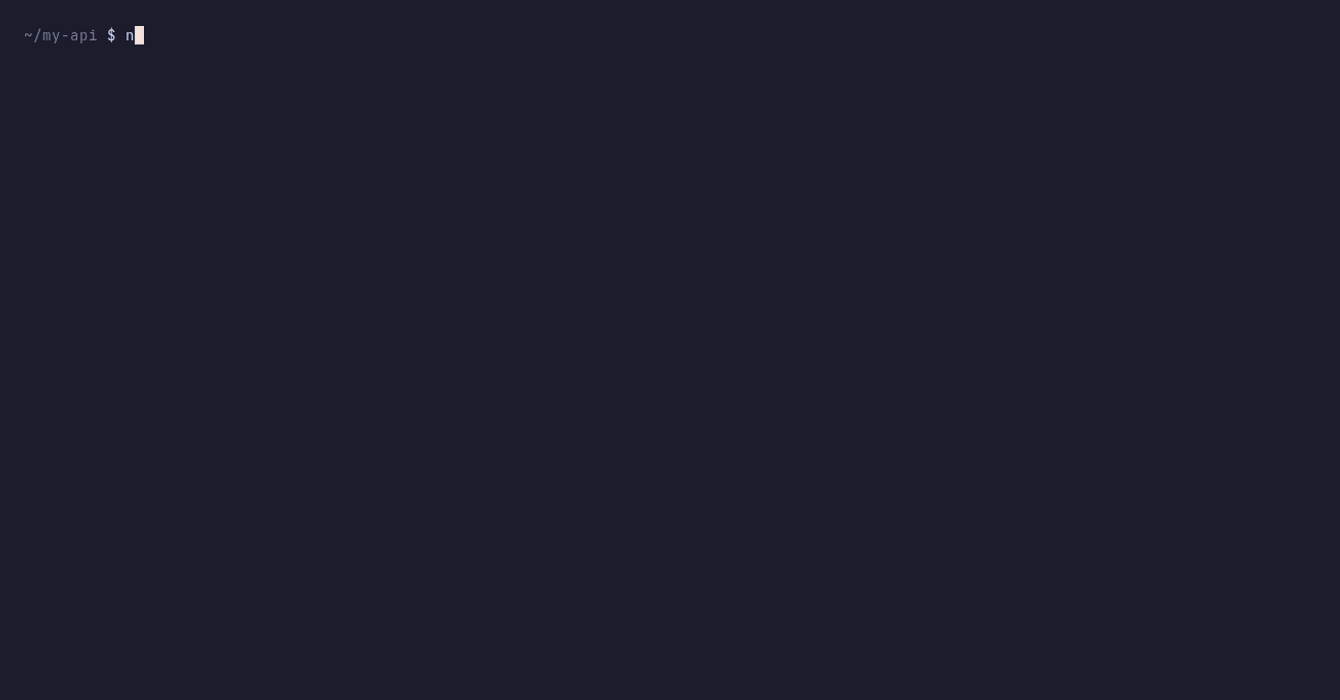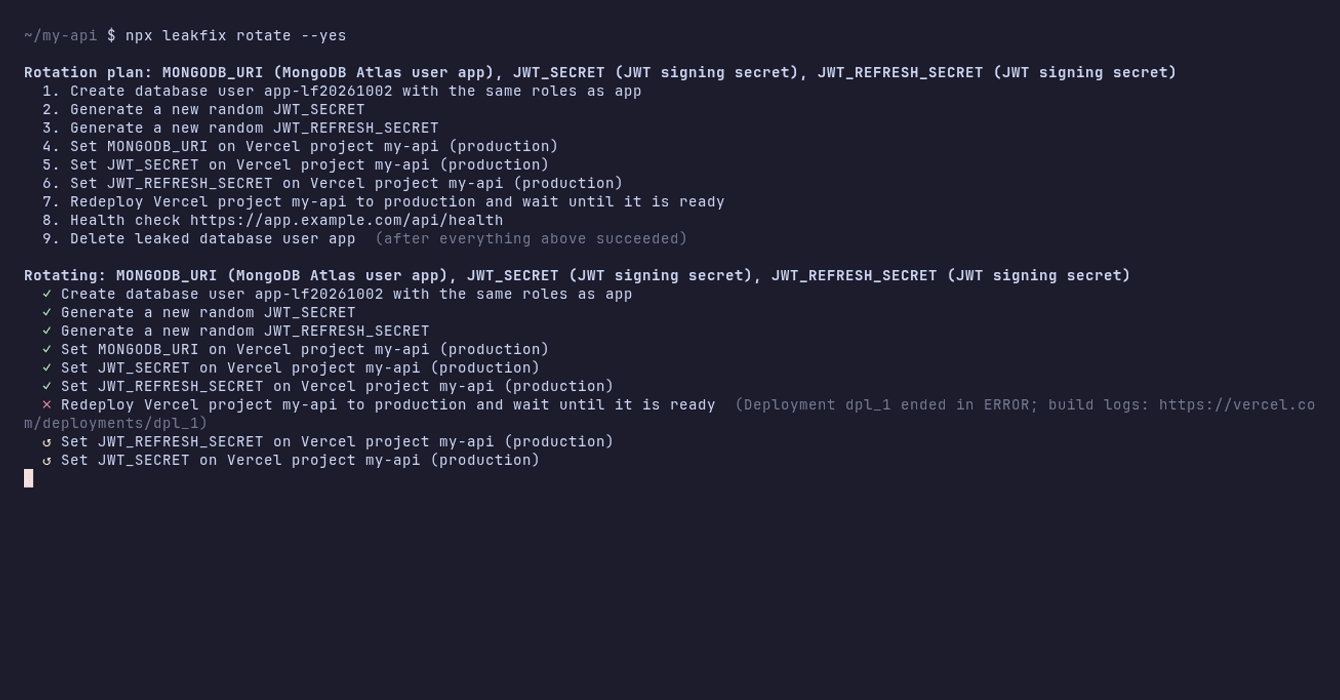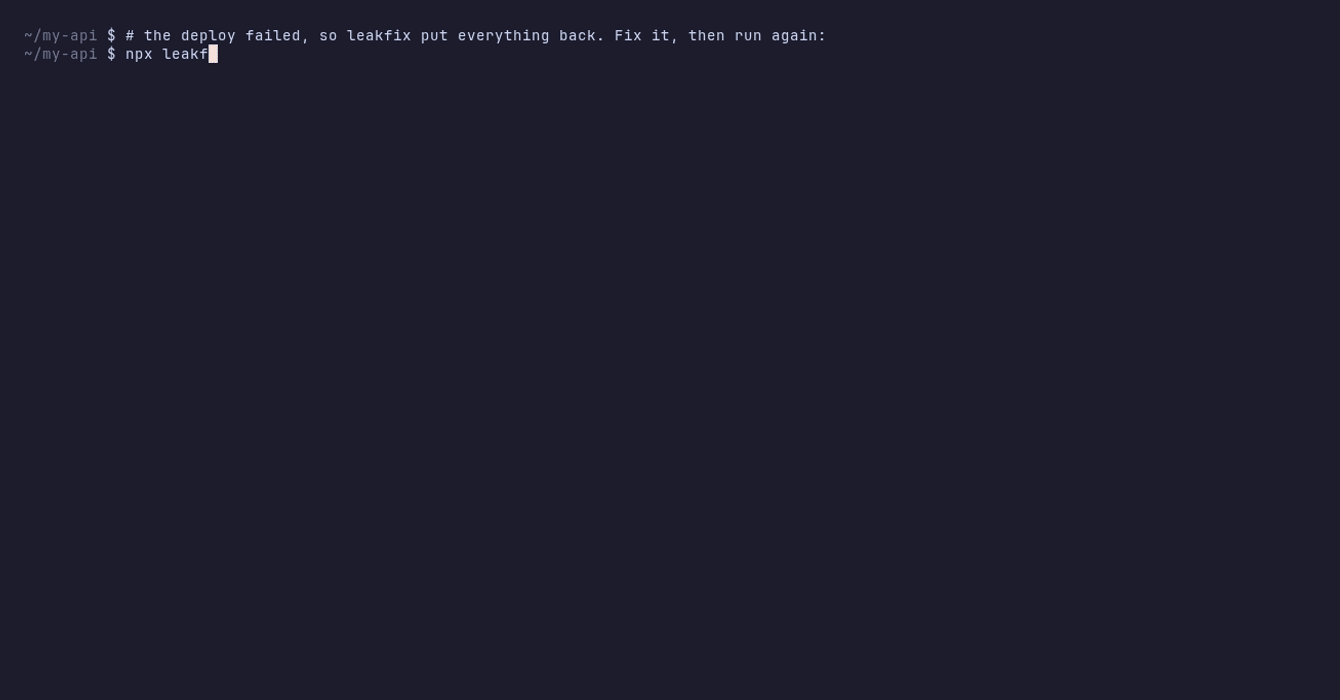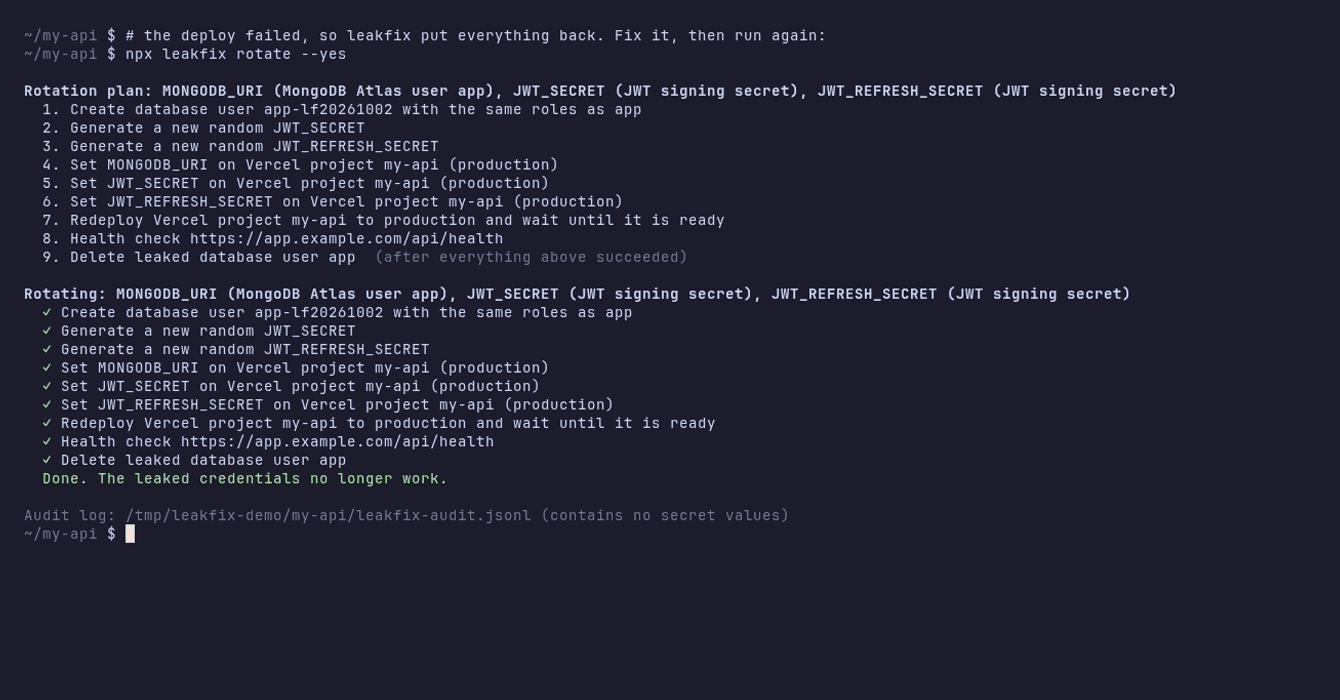
If any step fails, the completed steps are undone in reverse: variables get their old values back, production is redeployed on the old config, and the new credential is deleted. The app keeps running the whole time.
Once revoking starts, never roll back
Rolling back at that point would mean pointing production at the leaked credential again. A test caught my first version doing exactly that, so this became a hard rule.
Test every failure against fake clouds
The tests run whole rotations against in-memory imitations of the Atlas, Vercel and Render APIs, and make them fail on purpose: a broken deploy, a failing health check, a blocked IP.
Prove it on real services
Green tests weren't trusted until the tool had rotated real secrets on a live Vercel app and a live Render service, including a deliberate rollback.
Read-only setup before any change
leakfix init finds the right project, checks every permission and explains exactly what's missing, without changing anything. Setup friction was the main reason people wouldn't use it.
One small interface per platform
A platform only has to read a variable, set it and redeploy. Vercel and Render share that interface, so adding Railway or Netlify is a single file.
What's built
scan
Finds secrets in a repo and whether git tracks them, with values masked on screen.
init
Detects the deployment and the Atlas project, checks access and writes the config.
rotate
Prints the plan as a dry run; with --yes, rotates with rollback on failure.
fix-repo
Stops tracking .env files, adds .gitignore entries and an .env.example with names only.
GitHub Action
Fails a pull request that commits a secret, before it reaches the main branch.
Shipping
Published on npm (npx leakfix), a Docker image, CI on Node 22 and 24, and releases published from a git tag with npm Trusted Publishing.
Results
- Rotated the leaked secrets of my own production app with zero downtime. The first two real runs failed (an Atlas IP allowlist, then a Vercel redeploy quirk), and both times leakfix rolled everything back on its own while the app stayed up.
- Rotation and rollback verified on a live Render service.
- 22 tests cover whole rotations, including failed deploys, failed health checks and rollbacks.
- Published on npm with a demo, a roadmap and a contributing guide for new platforms.
My role
- Designed and built it end to end, as a solo open-source project, with AI tools as a pair programmer.
- Ran the first real rotations on my own production app and fixed what they uncovered.
- Set up CI, the Docker image, npm releases and the launch write-up.